2026년 2월 28일 미국과 이스라엘의 이란 공격에는 사이버공격이 부가적인 공격이 아니라 연관된 공격으로 생각됩니다.
https://xcoolcat7.tistory.com/92172
2026년 2월 미국 이스라엘의 이란 공습 그리고 사이버 공격
2026년 2월 28일 (현지시간) 미국과 이스라엘은 이란을 공격합니다. 미국은 Operation Epic Fury, 이스라엘은 Operation Lion's Roar로 명명합니다. 미국-이란 전쟁 나무위키https://namu.wiki/w/%EB%AF%B8%EA%B5%AD-%EC%9D%B
xcoolcat7.tistory.com
이란의 반격(?)도 발견됩니다
3월 11일 한달라 (Handala)는 Stryker사를 해킹했다고 밝힙니다.
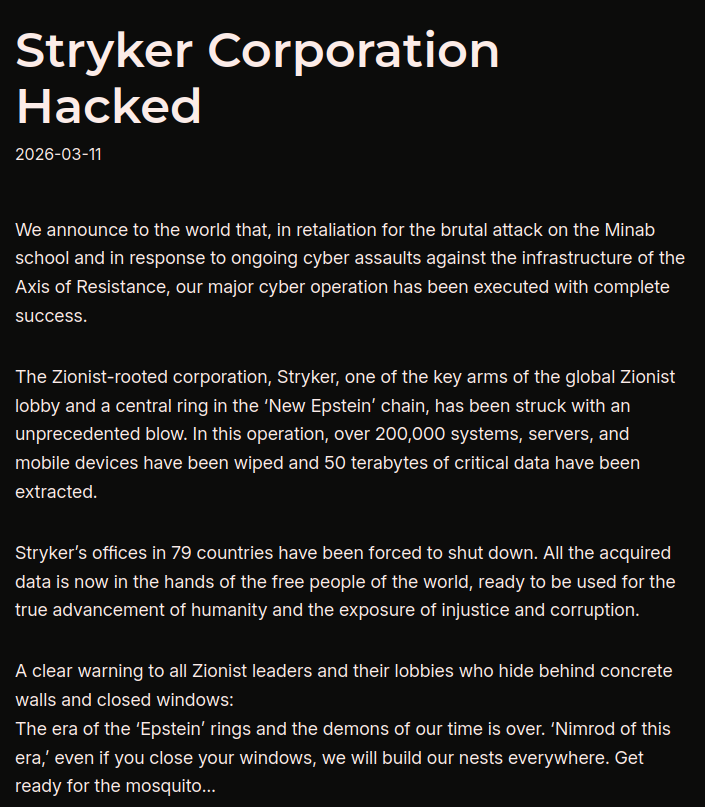
https://handala-hack.to/stryker-corporation-hacked/
Stryker Corporation Hacked – Handala Hack Team
We announce to the world that, in retaliation for the brutal attack on the Minab school and in response to ongoing cyber assaults against the infrastructure of the Axis of Resistance, our major cyber operation has been executed with complete success. The Z
handala-hack.to
3월 19일 FBI는 Handala 사이트를 폐쇄합니다.
Justice Department Disrupts Iranian Cyber Enabled Psychological Operations (2026.03.19)
https://www.justice.gov/opa/pr/justice-department-disrupts-iranian-cyber-enabled-psychological-operations
Justice Department Disrupts Iranian Cyber Enabled Psychological Operations
Today, the Justice Department announced the seizure of four domains as part of an ongoing effort to disrupt hacking and transnational repression schemes conducted by the Islamic Republic of Iran’s Ministry of Intelligence and Security (MOIS). The affidav
www.justice.gov
Handala는 홈페이지 주소를 변경합니다.
Handala Hack Team – Free Palestine
In an incident that sent shockwaves through the Israeli intelligence apparatus, the personal email of Sima Shine, the former Deputy Director for Research of Mossad, former Head of the Iran Desk, and current leader of one of Israel’s most secretive intell
handala-team.to
단순 정보를 유출한게 아니라 Wiper를 이용해서 내부 데이터를 파괴했다고 합니다.
Medtech giant Stryker offline after Iran-linked wiper malware attack (2026.03.11)
Medtech giant Stryker offline after Iran-linked wiper malware attack
Leading medical technology company Stryker has been hit by a wiper malware attack claimed by Handala, an Iranian-linked and pro-Palestinian hacktivist group.
www.bleepingcomputer.com
Iran-Backed Hackers Claim Wiper Attack on Medtech Firm Stryker (2026.03.11)
https://krebsonsecurity.com/2026/03/iran-backed-hackers-claim-wiper-attack-on-medtech-firm-stryker/
Iran-Backed Hackers Claim Wiper Attack on Medtech Firm Stryker – Krebs on Security
A hacktivist group with links to Iran’s intelligence agencies is claiming responsibility for a data-wiping attack against Stryker, a global medical technology company based in Michigan. News reports out of Ireland, Stryker’s largest hub outside of the
krebsonsecurity.com
Cyberwarfare Iran-Linked Hacker Attack on Stryker Disrupted Manufacturing and Shipping (2026.03.13)
Iran-Linked Hacker Attack on Stryker Disrupted Manufacturing and Shipping
Evidence indicates that the attackers leveraged existing endpoint management software rather than malware to wipe devices.
www.securityweek.com
* 분석 정보
보안업체에서 관련 정보를 공개합니다
Insights: Increased Risk of Wiper Attacks
https://unit42.paloaltonetworks.com/handala-hack-wiper-attacks/
Insights: Increased Risk of Wiper Attacks
We are observing an increase of wiper attacks by the Iran-linked Handala Hack group (aka Void Manticore) through phishing and misuse of Microsoft Intune.
unit42.paloaltonetworks.com
“Handala Hack” – Unveiling Group’s Modus Operandi
https://research.checkpoint.com/2026/handala-hack-unveiling-groups-modus-operandi/
“Handala Hack” - Unveiling Group's Modus Operandi - Check Point Research
Key Findings Introduction Handala Hack, also tracked by Check Point Research as Void Manticore, is an Iranian threat actor that is known for multiple destructive wiping attacks combined with “hack and leak” operations. The threat actor operates several
research.checkpoint.com
* Handala 는 누구 ?
Handala 는 핵티비스트로 가장하고 있지만 이란 정보기관의 소행으로 추정된다고 합니다.
Dark Web Profile: Handala Hack
https://socradar.io/blog/dark-web-profile-handala-hack/
Dark Web Profile: Handala Hack
Not every hacktivist group is what it claims to be. Handala presents itself as a pro-Palestinian resistance collective, borrowing the name and imagery of a
socradar.io
Threat Overview - Handala Threat Group (2026.03.13)
https://www.intel471.com/blog/handala-threat-group
Handala Threat Group
An Iranian aligned threat group conducting destructive and espionage focused cyber operations against organizations in Israel and Western countries.
www.intel471.com
* 사건 후
모든 의료 기기는 안전하게 사용할 수 있지만 전자 주문 시스템은 여전히 작동하지 않으므로 고객은 영업 담당자를 통해 수동으로 주문해야 한다고 밝혔습니다.
공격자는 "20만 대 이상의 시스템, 서버 및 모바일 기기"를 초기화하고 50테라바이트의 데이터를 훔쳤다고 주장했지만, 조사 결과 데이터 유출의 흔적은 발견되지 않았다고 합니다.
(공격자는 과장하려고하고 피해 입은 쪽은 축소하려는 점을 고려해야합니다.)
Stryker attack wiped tens of thousands of devices, no malware needed
Stryker attack wiped tens of thousands of devices, no malware needed
Last week's cyberattack on medical technology giant Stryker was limited to its internal Microsoft environment and remotely wiped tens of thousands of employee devices.
www.bleepingcomputer.com
공격자가 악성코드를 사용하지 않았다고 하지만, 보안 업체 자료에 따르면 Wiper가 발견되었습니다.
Stryker says hospital tools are safe, but digital ordering systems still down after cyberattack
https://therecord.media/stryker-cyberattack-impact-iran
Stryker says hospital tools are safe, but digital ordering systems still down after cyberattack
Electronic ordering systems belonging to the medical device company Stryker are still down a week after a cyberattack believed to have wiped thousands of company devices of all information. The company said its digital products are safe for use.
therecord.media
'보안위협 (악성코드, 취약점) > Threat Actor' 카테고리의 다른 글
| 오퍼레이션 더블 배럴 (Operation Double Barrel) - 국가배후 해킹조직의 한국 공격 주의 권고 (0) | 2026.08.03 |
|---|---|
| 독일 경찰 갠드크랩 (GandCrab)과 REvil 관계자 신원 공개 (1) | 2026.04.13 |
| 북한 해킹 그룹의 협력 혹은 공유 ? - 인프라 공유 (0) | 2026.03.10 |
| Silk Typhoon (Hafnium) 그룹 관련 의심 중국인 쉬쩌웨이 (Xu Zewei) 체포 및 미국 송환 (2) | 2025.08.11 |
| 중국의 역습(?) 사이버공격 미국 NSA 와 대만 관계자 실명 공개 (2) | 2025.06.30 |