2025년 7월 18일 셰어포인트 취약점을 이용한 공격이 발견되었습니다. 관련 공격은 7월 7일부터 시작되었다고 합니다.
| SharePoint는 조직 내에서 팀워크를 용이하게 하고 문서 관리를 간소화하도록 설계된 공동 작업 플랫폼입니다. https://support.microsoft.com/ko-kr/sharepoint |
| 날짜 | 내용 |
| 07.14 | Pwn2Own Berlin 2025 에서 ToolShell CVE-2025-49706(스푸핑 문제)과 CVE-2025-49704(원격 코드 실행 결함) 발견 공개 |
| 07.18 | 온프라미스 SharePoint 취약점 (CVE-2025-53770) 이용한 공격 발견 (실제 공격은 7월 7월) |
| 07.20 | 마이크로소프트, 취약점 보안업데이트 제공 |
| 08.20 | 마이크로소프트, 중국의 MAPP 접근 축소 |
ToolShell 취약점
온프레미스 SharePoint 서버에 대한 무단 액세스를 허용하는 제로데이 취약점(CVE-2025-53770)입니다.
Microsoft SharePoint Server Remote Code Execution Vulnerability (CVE-2025-53770)
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-53770
Security Update Guide - Microsoft Security Response Center
msrc.microsoft.com
해당 취약점은 ToolShell 로도 불립니다.
ToolShell은 SharePoint 취약점 두 가지인 CVE-2025-49706(스푸핑 문제)과 CVE-2025-49704(원격 코드 실행 결함)에 지정된 이름으로, Pwn2Own Berlin 해킹 경연 대회에 참여한 연구원들이 5월에 Microsoft에 해당 취약점의 존재를 보고했습니다.
https://x.com/codewhitesec/status/1944743478350557232
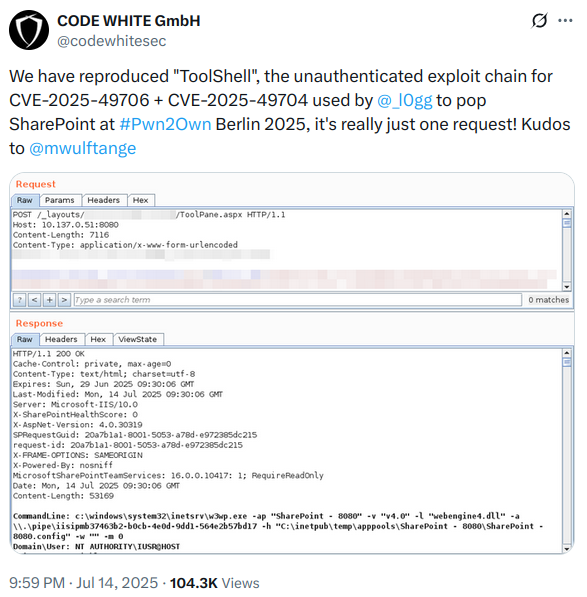
마이크로소프트는 2025년 7월 패치 때 포함했습니다만, 며칠 후 다른 연구원들이 해당 취약점을 기반으로 인증 없이도 원격 코드 실행이 가능한 실제 공격에 사용합니다. 이들은 CVE-2025-53770, CVE-2025-53771이 부여되었고 ToolShell의 실질적인 공격 버전으로 분류하고 있습니다.
7월 20일 패치가 발표됩니다.
Microsoft Fix Targets Attacks on SharePoint Zero-Day (2025.07.21)
https://krebsonsecurity.com/2025/07/microsoft-fix-targets-attacks-on-sharepoint-zero-day/
Microsoft Fix Targets Attacks on SharePoint Zero-Day – Krebs on Security
On Sunday, July 20, Microsoft Corp. issued an emergency security update for a vulnerability in SharePoint Server that is actively being exploited to compromise vulnerable organizations. The patch comes amid reports that malicious hackers have used the Shar
krebsonsecurity.com
Microsoft Patches ‘ToolShell’ Zero-Days Exploited to Hack SharePoint Servers (2025.07.22)
영향
전 세계 300개 이상의 조직에서 4,600건 이상의 CVE 침해 시도가 발생하여 CVE가 광범위하게 악용되었다고 합니다. 지금까지 최소 400개의 SharePoint 서버가 해킹된 것으로 확인되었습니다.
SharePoint Under Siege: ToolShell Exploit (CVE-2025-49706 & CVE-2025-49704) (2025.07.19)
https://research.eye.security/sharepoint-under-siege/
SharePoint 0-day uncovered (CVE-2025-53770)
On the evening of July 18, 2025, Eye Security was the first in identifying large-scale exploitation of a new SharePoint remote code execution (RCE) vulnerability chain in the wild. Read how we found it & what we did afterwards.
research.eye.security
Global hack on Microsoft product hits U.S., state agencies, researchers say (2025.07.20)
https://www.washingtonpost.com/technology/2025/07/20/microsoft-sharepoint-hack/
랜섬웨어 갱 같은 사이버범죄 조직도 이 취약점을 이용합니다.
Warlock 랜섬웨어 배포에도 이용되었습니다.
Disrupting active exploitation of on-premises SharePoint vulnerabilities (2025.07.22)
Disrupting active exploitation of on-premises SharePoint vulnerabilities | Microsoft Security Blog
Microsoft has observed two named Chinese nation-state actors, Linen Typhoon and Violet Typhoon, exploiting vulnerabilities targeting internet-facing SharePoint servers. In addition, we have observed another China-based threat actor, tracked as Storm-2603,
www.microsoft.com
Microsoft says some SharePoint server hackers now using ransomware (2025.07.23)
https://www.reuters.com/sustainability/boards-policy-regulation/microsoft-says-some-sharepoint-server-hackers-now-using-ransomware-2025-07-23/
ToolShell Attacks Hit 400+ SharePoint Servers, US Government Victims Named (2025.07.24)
ToolShell: a story of five vulnerabilities in Microsoft SharePoint (2025.07.25)
https://securelist.com/toolshell-explained/117045/
ToolShell: a story of five vulnerabilities in Microsoft SharePoint
Explaining the ToolShell vulnerabilities in SharePoint: how the POST request exploit works, why initial patches can be easily bypassed, and how to stay protected.
securelist.com
The National Reconnaissance Office (NRO)
https://www.theregister.com/2025/07/28/infosec_in_brief/
Spy sat agency breached – insists no secrets spilled
Infosec in brief: Plus, leak site for BlackSuit seized, Tea spilt, and avoid crime if you've got a famous dad
www.theregister.com
배후
7월 22일부터 중국 해커들이 사용했다고 보도됩니다.
마이크로소프트는 Linen Typhoon, Violet Typhoon, Storm-2603 등이 취약점을 이용했다고 합니다.
Microsoft says Chinese hacking groups exploited SharePoint vulnerability in attacks (2025.07.22)
https://www.cnbc.com/2025/07/22/microsoft-sharepoint-chinese-hackers.html
Microsoft says Chinese hacking groups exploited SharePoint vulnerability in attacks
Two Chinese nation-state actors and one China-based threat actor have tried to exploit the vulnerability for weeks, Microsoft said.
www.cnbc.com
A Failed Microsoft Security Patch Is the Latest Win for Chinese Hackers (2025.07.24)
https://www.wsj.com/tech/cybersecurity/microsoft-china-cyberattacks-patch-aa25b2a8
Microsoft servers hacked by Chinese groups, says tech giant
https://www.bbc.com/news/articles/c4gdnz1nlgyo
Microsoft servers hacked by Chinese state-backed groups, firm says
The US tech giant is recommending some users install security updates after the data breach.
www.bbc.com
Storm-2603 Exploits SharePoint Flaws to Deploy Warlock Ransomware on Unpatched Systems (2025.07.24)
https://thehackernews.com/2025/07/storm-2603-exploits-sharepoint-flaws-to.html
의혹
2025년 7월 25일, 블룸버그는 마이크로소프트가 자사의 Microsoft Active Protections Program(MAPP) 유출로 인해 중국 해커들이 패치가 출시되기 전에 SharePoint 취약점을 악용했는지 조사하고 있다고 보도했습니다.
When Privileged Access Falls into the Wrong Hands: Chinese Companies in Microsoft’s MAPP Program (2025.08.01)
https://nattothoughts.substack.com/p/when-privileged-access-falls-into
When Privileged Access Falls into the Wrong Hands: Chinese Companies in Microsoft’s MAPP Program
Chinese companies face conflicting pressures between MAPP’s non-disclosure requirements and domestic policies that incentivize or mandate vulnerability disclosure to the state.
nattothoughts.substack.com
결국 마이크로소프트는 중국 연구가들에게 MAPP로 사전에 제공되던 취약점 정보 접근을 제한했습니다.
Microsoft scales back Chinese access to cyber early warning system (2025.08.21)
참고
All posts tagged "ToolShell"
https://www.securityweek.com/topics/toolshell/
Microsoft pins on-prem SharePoint attacks on Chinese threat actors (2025.07.22)
https://www.helpnetsecurity.com/2025/07/22/microsoft-pins-sharepoint-attacks-cve-2025-53770/
Microsoft pins on-prem SharePoint attacks on Chinese threat actors - Help Net Security
Microsoft and various security firms have begun sharing details about the on-prem SharePoint attacks they have detected.
www.helpnetsecurity.com
MS쉐어포인트 해킹 사태, 아 참! 전자기기를 사면 백도어를 같이 줘요! (2025.08.01)
https://www.youtube.com/watch?v=xuvSmCAnHKo
'보안위협 (악성코드, 취약점)' 카테고리의 다른 글
| BadCam - 웹캠 펌웨어 변조 공격 (0) | 2025.12.15 |
|---|---|
| 식당 로봇 해킹 가능성 - 로봇에 대한 보안 문제는 이제 시작일 듯 (0) | 2025.10.13 |
| 사이버공격으로 러시아 아에로플로트 (Aeroflot) 항공사 운항 장애 (4) | 2025.08.04 |
| 시그널(Signal) 스캠 (피싱) ... 서비스 사칭 (0) | 2025.05.19 |
| 북한 IT 인력이 사용한 VPN IP 리스트 (0) | 2025.04.08 |